What does GDPR compliance mean for AI agents?
GDPR-compliant AI means: you process personal data with AI only on a legal basis (Art. 6 GDPR), for a specific purpose and securely (Art. 5, Art. 32 GDPR), and data subjects can exercise their rights (Art. 15–22 GDPR) towards the AI agent as well. The obligations of the EU AI Act are added on top.
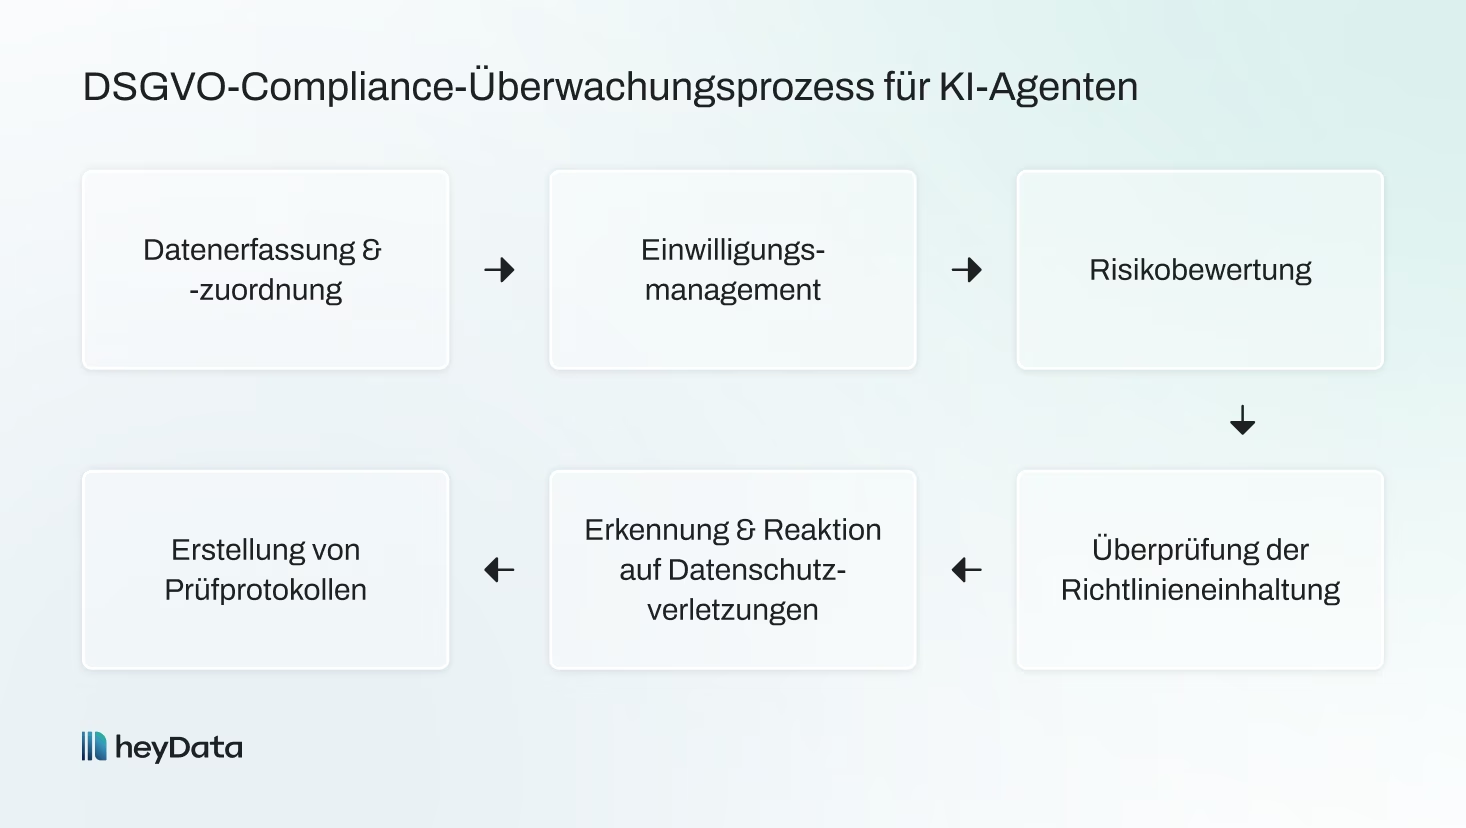
This is a process that runs from planning to ongoing monitoring. Art. 25 GDPR requires data protection by design and by default: put suitable measures in place when you choose the means of processing and during the processing itself.
Do AI agents need to be GDPR-compliant?
Yes. If your AI agent processes personal data and your company operates in the EU or targets users in the EU, the GDPR applies to it.
An AI agent is a system that performs tasks independently based on inputs, rules and training, for example answering customer requests, enriching CRM data or making recommendations. In doing so, it often processes personal data such as names, email addresses, behavioural logs or IP addresses. Indirect processing also falls under the GDPR. A concrete example of an agent's functions and compliance risks is OpenClaw. Voice agents raise the same questions, see our deep dive on data privacy in voice AI.
Which 7 principles under Art. 5 GDPR apply to AI agents?
Build the principles of Art. 5 GDPR directly into how your AI agents work.
1. Lawfulness, fairness, transparency (Art. 5(1)(a))
- Document a legal basis under Art. 6 GDPR for every processing activity, e.g. performance of a contract, legitimate interest or consent.
- Explain in your privacy policy when AI agents are used, what data they use and for what purpose.
- Tell users that they are interacting with AI, e.g. “You are now chatting with our virtual assistant.” From 2 August 2026, Art. 50(1) AI Act requires providers to make this recognisable, unless it is obvious to a reasonably well-informed person.
2. Purpose limitation (Art. 5(1)(b))
A new purpose requires a new assessment and, where necessary, a new legal basis.
- Define the agent's purpose and document it internally and in your privacy policy.
- Limit access to the data the agent needs for its main function. A support bot, for example, does not use marketing data as long as there is no legal basis for it.
- Reassess new integrations and check whether the purpose has gradually shifted.
3. Data minimisation (Art. 5(1)(c))
Give the agent only the data fields it needs and remove unnecessary or sensitive fields such as date of birth. A chatbot for resetting passwords only needs the email address. Review data flows regularly.
4. Accuracy (Art. 5(1)(d))
Check input data for plausibility and currency, update important fields such as job titles regularly and set up feedback loops so that errors are corrected quickly.
5. Storage limitation (Art. 5(1)(e))
Set retention periods for each purpose, state them in your privacy policy and set up automatic deletion, e.g. after 30 or 60 days.
6. Integrity and confidentiality (Art. 5(1)(f))
Which security measures are appropriate is determined by Art. 32(1) GDPR, taking into account the state of the art, implementation costs and risk. The provision mentions encryption, among other measures, but does not prescribe a specific method.
- Encrypt data in transit and at rest, e.g. with TLS and AES-256 (examples, not a GDPR requirement).
- Use role-based access controls and separate sensitive data: a recommendation agent, for example, does not need access to credit card data.
- Monitor the agent for suspicious activity.
7. Accountability (Art. 5(2))
You must be able to demonstrate that your agent complies with the principles. Document decision logic, inputs and models (see AI documentation requirements), list the agent in your record of processing activities (Art. 30 GDPR) where you are required to keep one, and appoint an internal person responsible.
How do you implement data subject rights in AI agents?
Your AI agent must be designed so that users can exercise their rights easily.
1. Right of access (Art. 15)
Users can find out which data is processed, for what purpose and by whom, and, for automated decisions, the logic involved. Keep structured logs, create clear access reports and provide a form or dashboard.
2. Right to rectification (Art. 16)
Corrections must reach all systems promptly. Prioritise them where incorrect data can lead to wrong decisions.
3. Right to erasure (Art. 17)
Set up complete deletion processes, including logs, backups and training data, and exclude deleted data from future model training. Our article on the right to be forgotten for AI explains why this is particularly difficult for AI models. For training data, see also how to train AI models with personal data.
4. Right to object (Art. 21)
Users can object to processing that is based on legitimate interest and can refuse direct marketing, including profiling, at any time. Offer opt-outs directly in the interaction and adjust the agent's behaviour (no personalisation, anonymised inputs where appropriate).
5. Automated decisions (Art. 22)
Data subjects have the right not to be subject to a decision based solely on automated processing that produces legal effects or similarly significantly affects them (Art. 22(1) GDPR). Exceptions are contractual necessity, authorisation by law and explicit consent (para. 2). For contract and consent, you must at least enable human intervention, the expression of the data subject's point of view and the contesting of the decision (para. 3). If an agent automatically rejects applicants, for example, a human review must be possible. See our article on AI in recruiting.
Do you need a DPIA for your AI agent (Art. 35 GDPR)?
It depends on the risk. You need a data protection impact assessment (DPIA) under Art. 35(1) GDPR where processing, in particular using new technologies, is likely to result in a high risk to the rights and freedoms of natural persons. Art. 35(3) names as examples a systematic and extensive evaluation of personal aspects based on automated processing, including profiling, with significant effects (point (a)), and large-scale processing of special categories of data (point (b)). Whether your agent falls under this is for you to assess case by case.
How do you monitor an AI agent on an ongoing basis?
GDPR compliance does not end at go-live. If your agent uses external APIs, such as a language model, those providers are usually processors.
- Conclude a data processing agreement (DPA) with them under Art. 28 GDPR. It covers, among other things, the subject matter, duration, nature and purpose of the processing as well as the security measures.
- Check whether data is transferred to third countries such as the US and safeguard these transfers. For choosing the deployment, see our article on US cloud, EU cloud or on-prem AI deployment.
- Review providers regularly, e.g. with heyData's vendor risk management.
- Log data access, processing, decisions and errors in a tamper-proof way (storage limitation applies here too) and respond quickly to anomalies.
- Review your DPIA, security measures and documentation at least annually and keep an eye on new guidance from data protection authorities on AI.
What does the EU AI Act require of AI agents (as of 2 November 2026)?
For AI agents, AI literacy (Art. 4) and transparency (Art. 50) are particularly relevant, and depending on the use case also the high-risk rules. The EU AI Act complements the GDPR but does not replace it – both must be met. Status: 2 November 2026.
| Topic | Rule | Applies from | What you need to do |
|---|---|---|---|
| Legal basis, principles, security | Art. 5, 6, 32 GDPR | already applies | Document a legal basis, implement the principles and risk-appropriate security. |
| Processor agreements | Art. 28 GDPR | already applies | Conclude a DPA with AI providers. |
| Data protection impact assessment | Art. 35 GDPR | already applies | Carry out in advance where the risk is likely to be high. |
| Prohibited AI practices | EU AI Act | since 2 Feb 2025 | Check whether your agent is affected, e.g. through emotion recognition in the workplace. |
| AI literacy | Art. 4 AI Act | since 2 Feb 2025 | Take measures to support the AI literacy of your staff; you do not have to guarantee a specific level. More: AI literacy. |
| Transparency | Art. 50 AI Act | from 2 Aug 2026 | Make it recognisable that users interact with AI (para. 1); mark synthetic content in a machine-readable format (para. 2, providers). |
| Marking for legacy systems | Art. 50(2) AI Act | from 2 Dec 2026 if the system was placed on the market before 2 Aug 2026 | Implement the marking by then. |
| High-risk AI (Annex III) | Chapter III AI Act | from 2 Dec 2027 | Risk management, documentation and human oversight, e.g. for agents in HR, lending or healthcare. |
| High-risk AI in products (Annex I) | Chapter III AI Act | from 2 Aug 2028 | As for Annex III, if the agent is part of a regulated product. |
Regulation (EU) 2026/1744 (“Digital Omnibus on AI”) has been in force since 27 July 2026 and postponed the high-risk deadlines (Annex III to 2 December 2027, Annex I to 2 August 2028). Sources: the European Commission, Cuatrecasas, artificialintelligenceact.eu. For background, see our article on the Digital Omnibus.
Check your agent's risk class with our checklist for classifying AI tools and the article on risk analysis for AI systems. Clarify whether you are provider or deployer – your obligations depend on it – and set out rules in an AI policy.
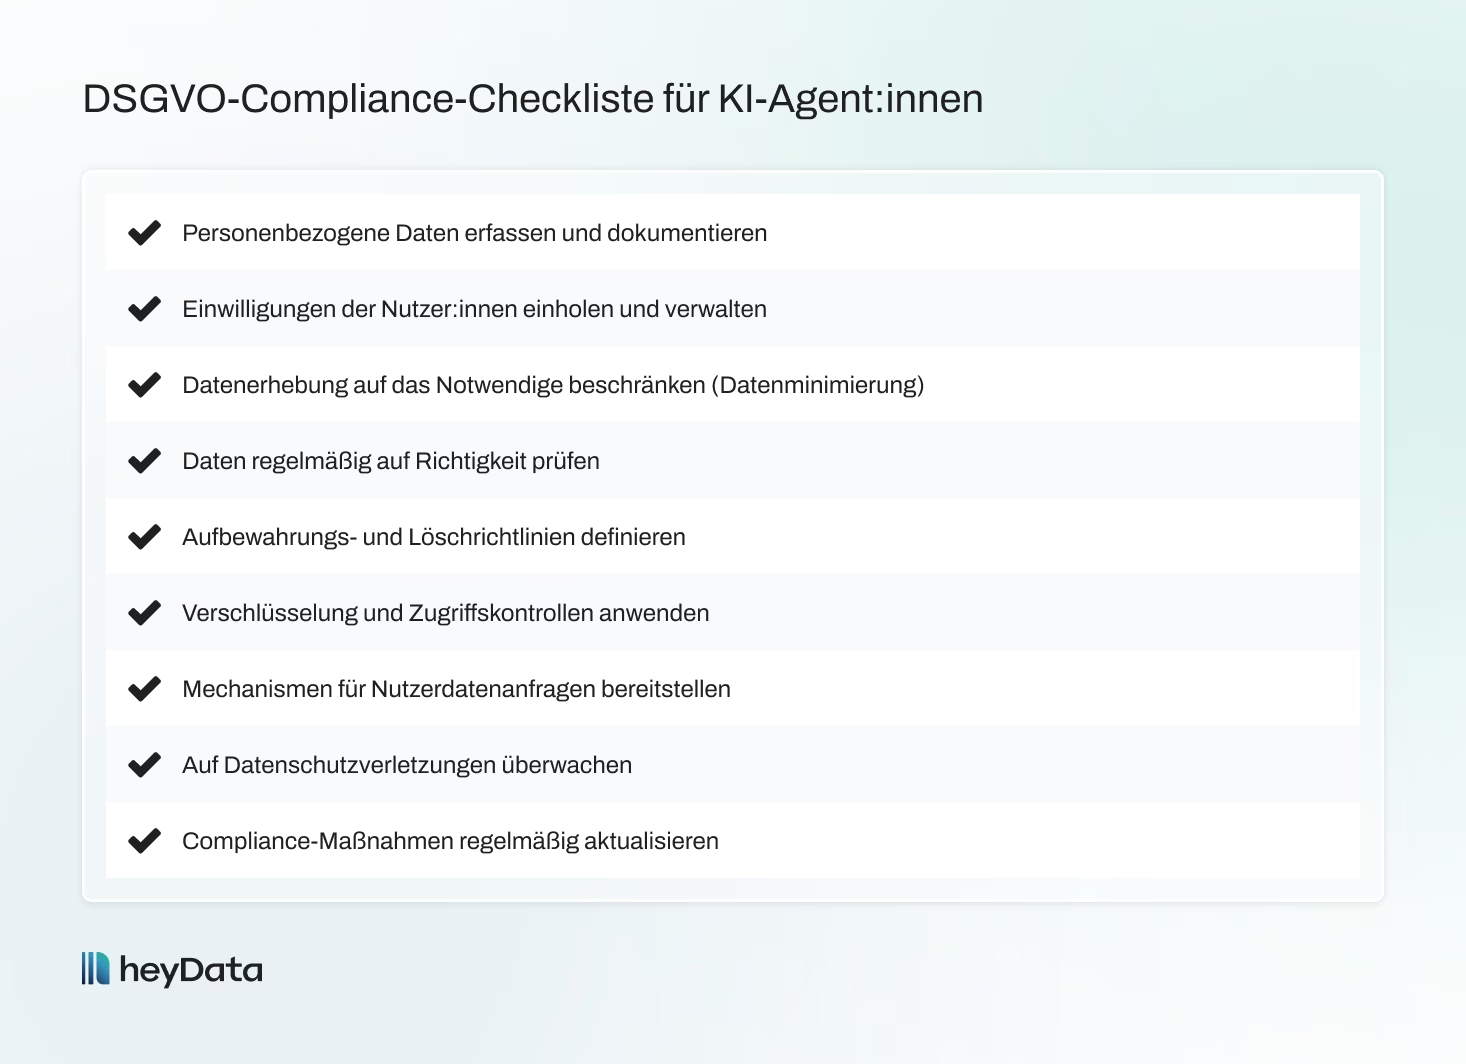
How do you check your AI agent? The tick-off checklist
- ☐ Legal basis documented for each processing activity
- ☐ Purpose defined, data access limited
- ☐ Users informed about the use of AI
- ☐ Retention periods and automatic deletion defined
- ☐ Security measures implemented in line with the risk
- ☐ Processes for access, rectification, erasure and objection
- ☐ Human review for automated decisions
- ☐ DPA with AI providers, third-country transfers safeguarded
- ☐ DPIA assessed
- ☐ Logging, monitoring and annual review in place
- ☐ AI literacy supported, risk class checked, responsible person appointed
Don't miss an update.
New laws, deadlines, and practical tips delivered straight to your inbox – once a month, no spam.
Conclusion
GDPR compliance for AI agents is complex – but essential.
From the legal basis, data minimisation, transparency and deletion routines to data subject rights, monitoring and vendor management: your responsibility does not end at go-live. The EU AI Act adds further obligations that you should consider from the start.
The benefits:
- lower legal risk
- more trust from your users
- a better user experience
- a clear signal of responsible innovation
With heyData's all-in-one compliance solution, you implement the GDPR and the EU AI Act for your AI systems in a structured way – with automated audits, DPIA templates and vendor monitoring.
Take the first step towards GDPR-compliant AI agents. Book a demo now!
EU AI Act: Guide to AI Compliance | heyData
Learn what the EU AI Act requires of companies and how to manage AI risks, documentation, oversight, and governance in a structured way.

Free & no obligation
FAQ
What is AI agent GDPR compliance?
What is AI agent GDPR compliance?
It means that AI systems processing personal data meet the requirements of the GDPR, including legal basis, security, transparency, and user rights.
Does my AI agent need a DPIA (Data Protection Impact Assessment)?
Does my AI agent need a DPIA (Data Protection Impact Assessment)?
It depends on the risk. Under Art. 35(1) GDPR you need a DPIA where the processing is likely to result in a high risk to the rights and freedoms of natural persons. Art. 35(3) names as examples, among others, extensive automated evaluation of personal aspects including profiling with significant effects (point (a)) and large-scale processing of special categories of data (point (b)). The DPIA helps identify and minimise risks early on.
Are AI agents allowed to make automated decisions?
Are AI agents allowed to make automated decisions?
Only under the conditions of Art. 22 GDPR: contractual necessity, authorisation by law or explicit consent. For contract and consent, data subjects must at least be able to obtain human intervention, express their point of view and contest the decision (Art. 22(3)).
How do I ensure my AI agent respects data subject rights?
How do I ensure my AI agent respects data subject rights?
Offer simple mechanisms for access, rectification, erasure, and objection. The agent must be able to adjust data processing when a right is exercised.
Which security measures does the GDPR require for AI agents?
Which security measures does the GDPR require for AI agents?
Art. 32(1) GDPR does not prescribe specific measures or methods. You must take appropriate technical and organisational measures that account for the state of the art, implementation costs, the nature, scope and purposes of the processing and the risk. The provision mentions encryption and pseudonymisation, among other measures. Typical for AI agents are encryption (e.g. TLS and AES), role-based access, monitoring, logging and anomaly detection. You should segment and well protect sensitive data.
How does the EU AI Act differ from the GDPR?
How does the EU AI Act differ from the GDPR?
The GDPR protects personal data. The EU AI Act regulates risk-based requirements for AI systems. High-risk agents must comply with both regulations.